 Brian Vermeer
3,969 views
Use Query Parameterization to Prevent Injection
Tip: By distinguishing between the SQL code and the parameter data, the query can’t be hijacked by malicious input.
 Brian Vermeer
3,969 views
Tip: By distinguishing between the SQL code and the parameter data, the query can’t be hijacked by malicious input.
Brian Vermeer
6,240 viewsIf you need to Deserialize an inputstream yourself, you should use an ObjectsInputStream with restrictions.
Brian Vermeer
13,129 viewsWith XML eXternal Entity (XXE) enabled, it is possible to create a malicious XML, and read the content of an arbitrary file on the machine.
Brian Vermeer
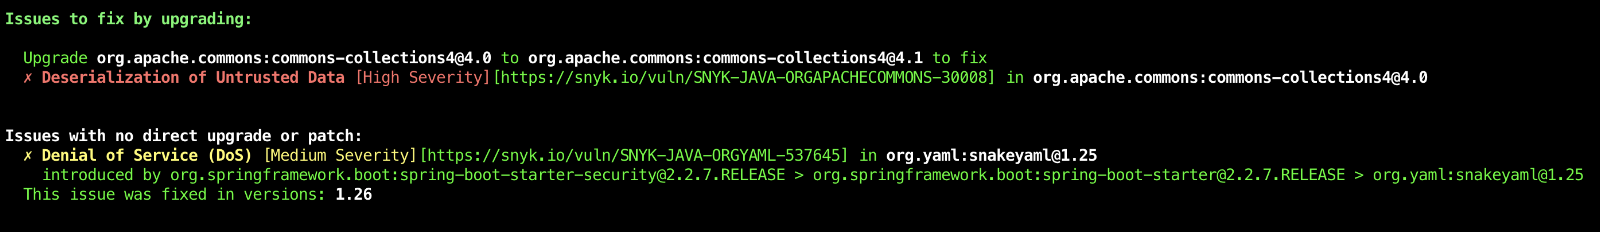
7,048 viewsIn this article, I will explain how you can fix vulnerabilities in third-party libraries when using Maven, even when it is not obvious.