 Brian Vermeer
3,116 views
How Chat Memory Manipulation Can Ruin Your AI System
Did you know that by tampering with chat history, you're able to make LLMs respond and execute functions that are out of policy?
Brian Vermeer
3,116 viewsDid you know that by tampering with chat history, you're able to make LLMs respond and execute functions that are out of policy?
 Gerrit Grunwald
4,982 views
Recently Azul announced that AVD makes it possible to identify vulnerable components on a jar file level but also on class file level.
Brian Vermeer
3,436 viewsWe know that LLMs can and will make mistakes, and while enriching your prompts with the proper context can help align results with your …
 Jonathan Vila
2,430 views
Sonar Connect Amsterdam : learn about code quality and code security specially when using AI generated code.
Brian Vermeer
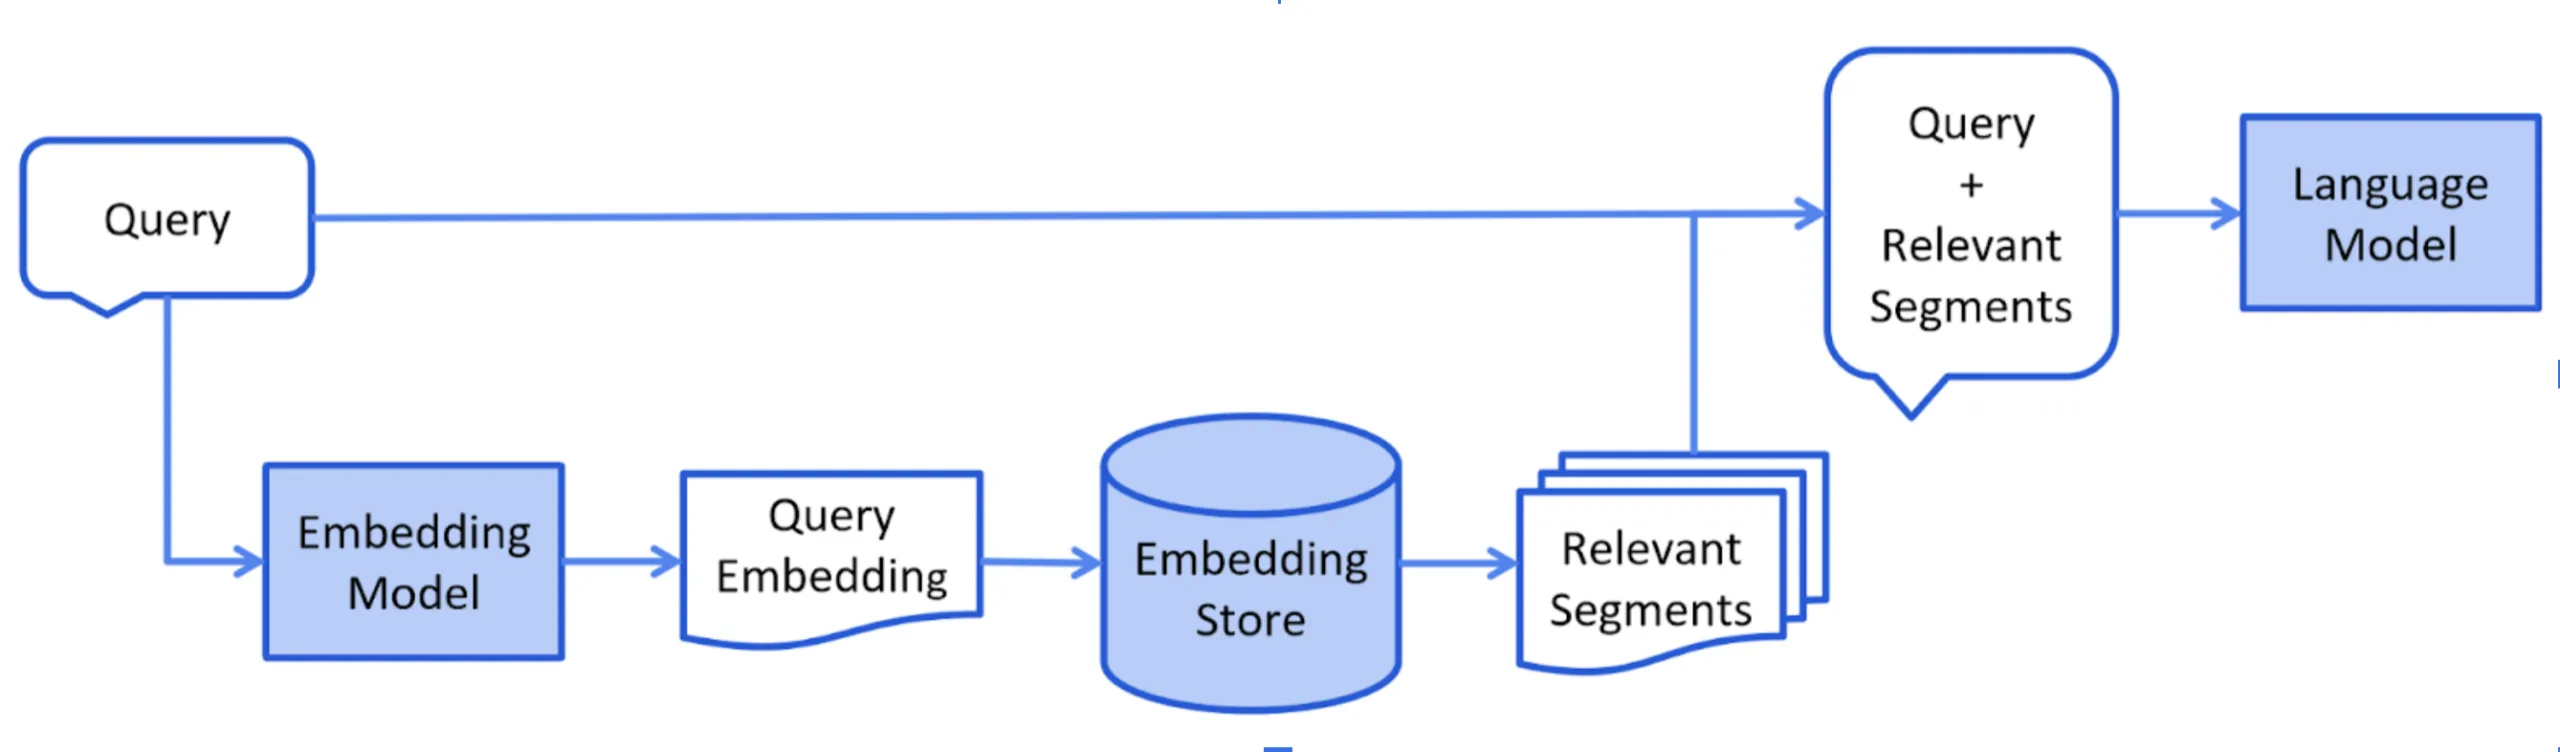
3,993 viewsThe implementation of RAG introduces security considerations. Risks such as prompt injection, data poisoning, access control gaps, and data …
 Steve Poole
4,372 views
As we settle into 2025, legislation around AI and cybercrime is no longer a distant threat or vague aspiration.
Brian Vermeer
4,952 viewsThis vulnerability highlights the importance of addressing supply chain security. If you aren't already, consider scanning your applications …
Brian Vermeer
3,490 viewsThe software bill of materials (SBOM) is quickly becoming an essential aspect of open source security and compliance. In this post, we'll …
Jonathan Vila
14,952 viewsCode reviews can be time-consuming and tedious. Let's explore their common pitfalls and how AI tools can revolutionize each phase of the …
 Simon Martinelli
2,969 views
Many companies use Microsoft 365, so letting users log in with their Microsoft account is a good choice. This blog post shows how to secure …