 Brian Vermeer
3,993 views
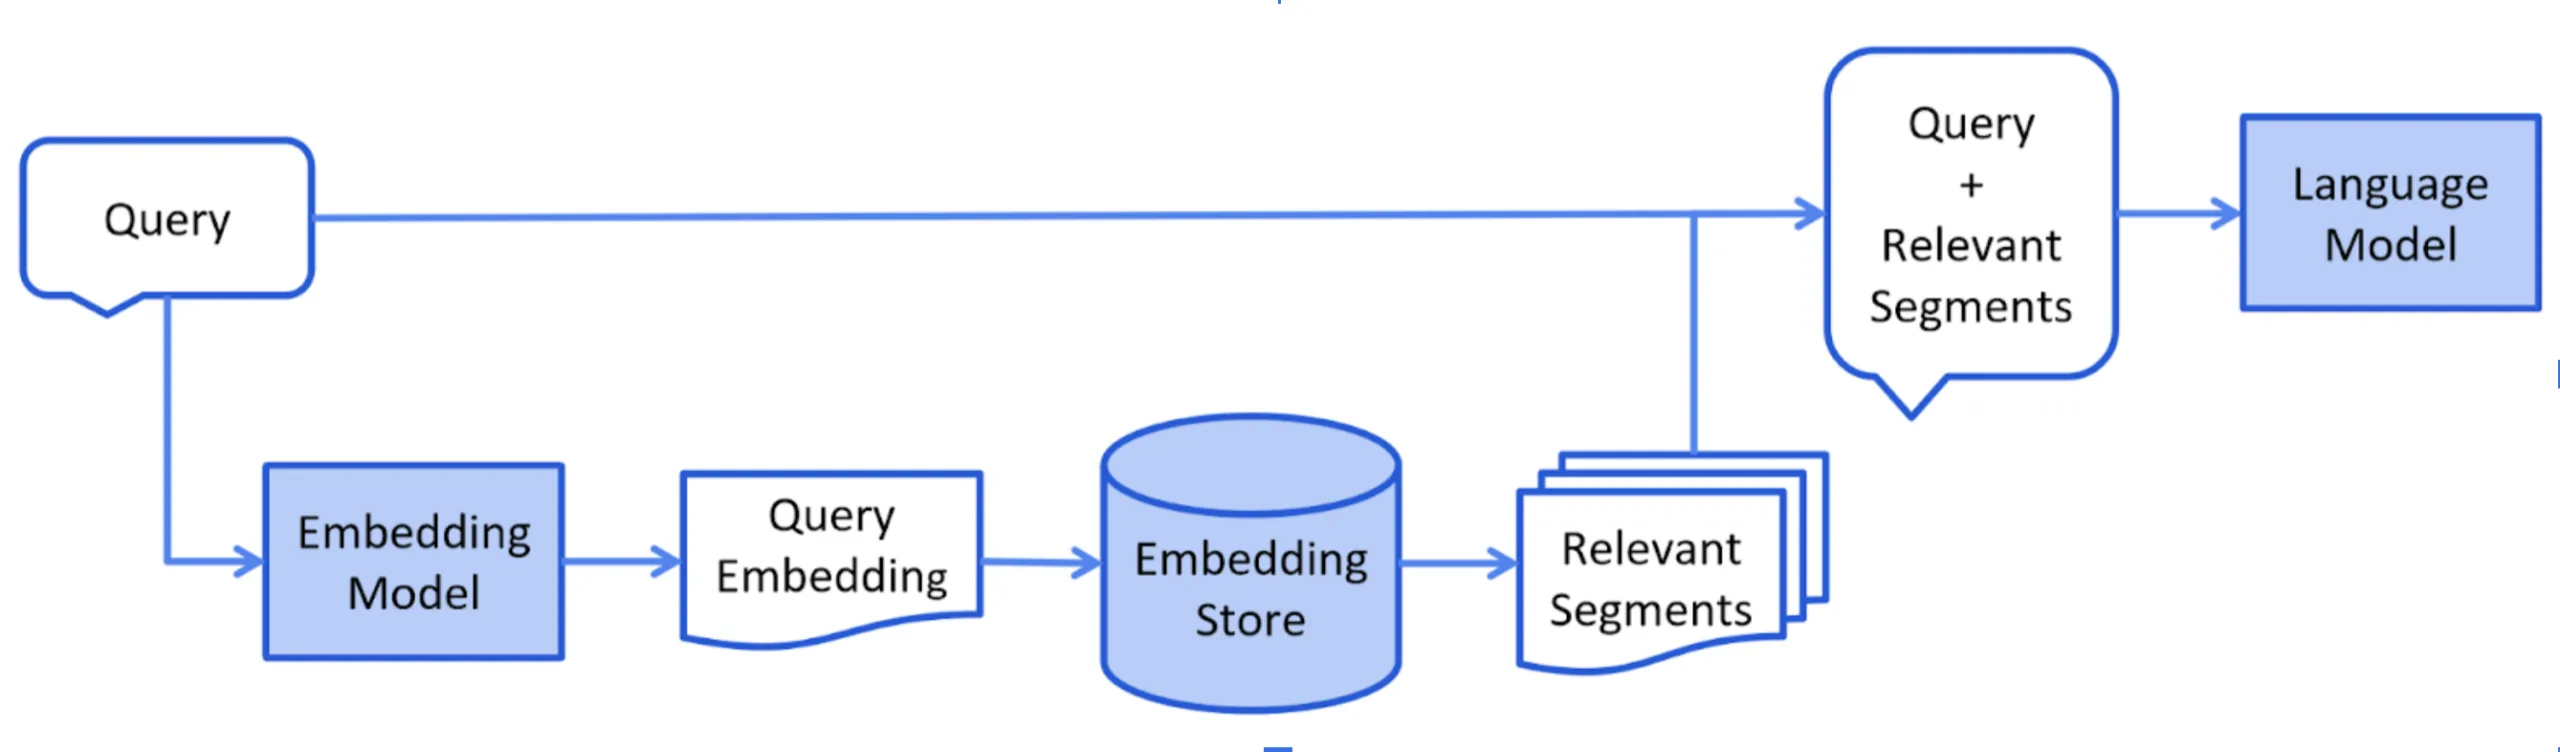
What is RAG, and How to Secure It
The implementation of RAG introduces security considerations. Risks such as prompt injection, data poisoning, access control gaps, and data …
Brian Vermeer
3,993 viewsThe implementation of RAG introduces security considerations. Risks such as prompt injection, data poisoning, access control gaps, and data …
Brian Vermeer
3,490 viewsThe software bill of materials (SBOM) is quickly becoming an essential aspect of open source security and compliance. In this post, we'll …
Brian Vermeer
6,856 viewsA lurking issue has been surprisingly overlooked: the continued use of vulnerable Log4j and Spring Framework versions in many projects.
Brian Vermeer
6,309 viewsNowadays, the security of your applications is just as important as the functionality they provide. Therefore, analyzing your code for …
Brian Vermeer
7,323 viewsEncryption is converting readable data or plaintext into unreadable data or ciphertext, ensuring that even if encrypted data is intercepted, …
Brian Vermeer
7,741 viewsKeeping your dependencies in check is crucial to ensure that your Spring Boot projects run smoothly and remain resilient in the face of …
Brian Vermeer
7,177 viewsAn in-depth exploration of utilizing JLink to optimize Docker image sizes, enhancing application security and performance.
Brian Vermeer
8,536 viewsIn December of last year, we reported CVE-2022-1471 to you. This unsafe deserialization problem could easily lead to arbitrary code …
Brian Vermeer
5,743 viewsBy taking a proactive approach to XSS prevention and using the right resources and tools, developers can help ensure the security and …
 Marit van Dijk
10,847 views
Did you know bots can automatically create pull requests to keep dependencies secure and up to date? Find out here!